Skip to content
View Largo-m's full-sized avatar
💭
I may be slow to respond.
💭
I may be slow to respond.

Block or report Largo-m

Block user

Prevent this user from interacting with your repositories and sending you notifications. Learn more about blocking users.

You must be logged in to block users.

Content in all repositories owned by your account will be closed.
Maximum 250 characters. Please don’t include any personal information such as legal names or email addresses. Markdown is supported. This note will only be visible to you.
Report abuse

Contact GitHub support about this user’s behavior. Learn more about reporting abuse.

Report abuse
Largo-m/README.md
Largo-m — security and privacy tooling with honest interfaces

Security and privacy tooling that is honest about what it does

Python · Qt / PySide6 · Windows internals · networking · developer tooling

GitHub followers Public repositories Sponsor


⚡ What I am building

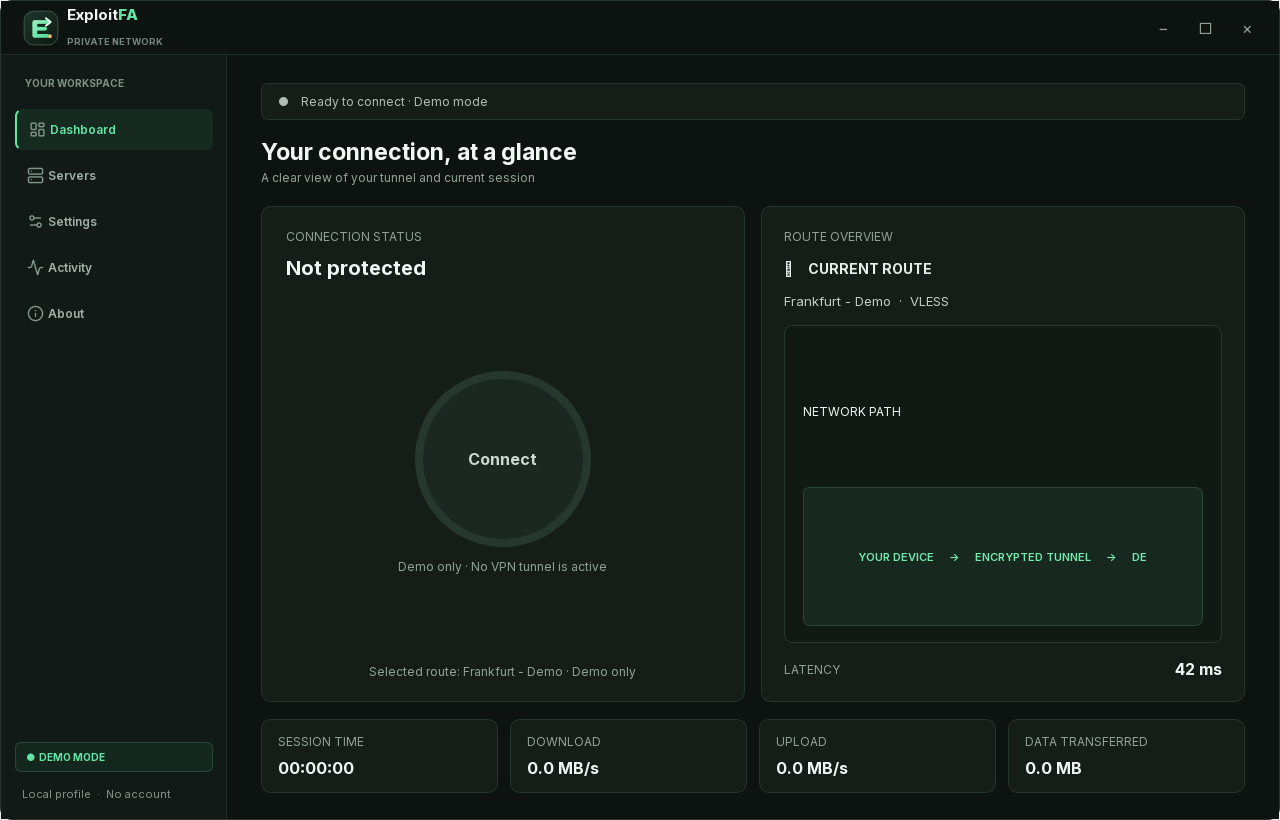
An English-first, left-to-right PySide6 desktop client for Xray VLESS on Windows. A real Qt interface, strict JSON configuration, checksum-verified builds, and a demo mode that never pretends your traffic is protected.

Reality · TLS · TCP · WebSocket · gRPC · live core · SOCKS5 + HTTP

ExploitFA stars ExploitFA release ExploitFA CI

ExploitFA dashboard

Parse, validate, build, convert, sort and redact VLESS / VMess / Trojan / Shadowsocks share links and base64 subscriptions. Pure standard library, no network code, safe to drop into CI.

$ vless-toolkit summary links.txt
total: 4  unique hosts: 4
by protocol:
  vless: 1  vmess: 1
  trojan: 1  shadowsocks: 1
by country:
  DE: 1  NL: 1  JP: 1  SG: 1

vless-toolkit stars vless-toolkit release

All-in-one AI-powered security toolkit: web, network and phishing tests with a modular CLI and GUI.

SecuSploitX stars

Also on GitHub

GhostTrace — multi-hop proxy chains · cyphisher — authorised phishing simulation · Ransomware-Analyzer — safe behaviour simulation · AutoCaption — local-first subtitles


🧭 How I build

Principle What it means in practice
Honest interfaces If a feature does not exist, the README says so and the UI says so. No fake "connected" states, no implied protection.
Tests before features Validation, parsing and process supervision are pure functions with real coverage — 122 tests in ExploitFA, 214 in vless-toolkit, headless in CI.
Small, boring dependencies Standard library first. Every unavoidable dependency is pinned, licensed and explained.
Reproducible builds Checksums for core binaries, SHA256SUMS.txt next to every artifact, releases built by a workflow from a tag.
Documentation as a feature Long READMEs with real screenshots and real command output, architecture notes that explain trade-offs, and tests that fail when a link breaks.

📈 By the numbers

122
tests · ExploitFA
214
tests · vless-toolkit
34
merged pull requests
3
CI jobs · every PR
0
telemetry endpoints

🧰 Toolbox

Python Qt Windows Linux PowerShell Git GitHub Actions Docker Ruff pytest PyInstaller


🏆 Achievements

Starstruck Quickdraw YOLO

Next up: Pull Shark (merged pull requests) and Pair Extraordinaire (co-authored commits).


📫 Reach me

Security tooling is for authorised testing only. Use it on systems you own or have explicit written permission to assess.

Pinned Loading

  1. SecuSploitX SecuSploitX Public

    Sploit -- All-in-one, AI-powered cybersecurity toolkit for web, network, and phishing tests. Modular, cross-platform, Docker-ready, with GUI & CLI. Open source by AUX-441 Team.

    HTML 41 7

  2. security-tools-hacking security-tools-hacking Public

    A powerful, modular Windows penetration testing framework with high coding scalability. Designed for security professionals and enthusiasts, this tool provides multiple modules for reconnaissance, …

    Python 12 2

  3. Userlvel5anonymous-Toolkit-Windows-ETH Userlvel5anonymous-Toolkit-Windows-ETH Public

    A comprehensive ethical hacking tool for network and system monitoring including screenshot capture, keylogging, camera access, and user location tracking. Designed for authorized cybersecurity ass…

    Python 10 1

  4. cyphisher cyphisher Public

    Cyphisher provides simulated phishing scenarios and awareness resources to help security teams train staff, validate controls, and run controlled exercises. Strictly for educational use and authori…

    HTML 13 2

  5. emotion-sentiment-classifier emotion-sentiment-classifier Public

    Understanding human emotions in text is crucial for many applications such as customer feedback analysis

    Python 6 1

  6. ExploitFA ExploitFA Public

    English-first, left-to-right PySide6 desktop client for Xray VLESS on Windows: live core mode, hot-reload JSON config, VLESS share-link import, SOCKS5/HTTP proxy, checksum-verified builds. No telem…

    Python 6 2