

Protect Loader is a shellcode loader written in pure golang designed to provide various security and evasion techniques for Go applications. It includes features such as shellcode loading, obfuscation, the use of indirect syscalls, and much more.
- Shellcode Loading: Loading shellcode using Early bird apc.
- GUI: User interface created with Fyne.
- Obfuscation: Code obfuscation with garble with optionnaly his controlflow (need to set the environment variable
GARBLE_EXPERIMENTAL_CONTROLFLOW=1). - Indirect Syscalls: Use of indirect syscalls by acheron for evasion.
- Api ashing: Acheron package have a integrated api hashing for evasion
- Bypass AMSI and EDR: Techniques to bypass AMSI and EDR.
- Admin Privileges Check: Check if admin privileges are enabled.
- Random Sleep: Adding random delays.
- Block Non-Microsoft DLLs: Blocking the injection of non-Microsoft DLLs.
- Phantom Technique: Suspension of event logs.
- PE file To Shellcode: The PE file is automatically transformed into a .bin using Donut and encoded using Shikata ga nai and encrypted using two layer of encryption (aes-cfb and xor)
- Key Encryption: The key generated is encrypted using XOR to prevent his extraction
-
🚧 = Priority Features
-
Create a GUI with Fyne
-
Enhance the shellcode injection (can always do better but waste of time)
-
Rework it to be more user-friendly (need to add option and bunch of things)
-
Make the code obfuscation with garble
-
Use indirect syscalls
-
Implement techniques to bypass AMSI and EDR
-
Check if admin privileges are enabled
-
Add random delays
-
Block the injection of non-Microsoft DLLs
-
Phantom technique to suspend event logs
-
Remove unhooking method (too monitored by EDR/AV,indirect syscalls is better)
-
Call Stack spoofing
-
Polymorphic code
-
Remote shellcode to avoid detection
-
Encrypt XOR and AES-CFB keys in
main.go -
Sign shellcode and loader with a certificate 🚧
-
Enchance the sleep duration (AV accelerate time in a sandbox)
-
Adding control flow obfuscation with garble
-
Support of shellcode file (.bin)
-
Anti debug/Anti vm
-
Spamming of admin prompt
-
Wiki
-
Add .ico support for the generated PE file
- Golang 1.24.4+
- CGO enable (you can use this to facilate the installation)
- Git
- Run the GUI.bat
- Select your PE file
- The GUI will compile it automatically (may take some time)
- In the GUI and subfolder there is a lot of PE file (exe) if you don't trust them,feel free to download them from their official repo.
- In complementary you can use this to obfuscate the IAT table with UPX and auto patch
- If you want to debug make sure to remove the elevation code from main.go
⚠️ IF you want to use Control flow obfuscation you will need set the environment variable GARBLE_EXPERIMENTAL_CONTROLFLOW=1
- Hooka Shellcode loader - for the code i use
- scriptchildie - Provide a amazing guide which help me a lot
- Taxmachine - Help me a lot for debugging or suggestions check out his github !

-
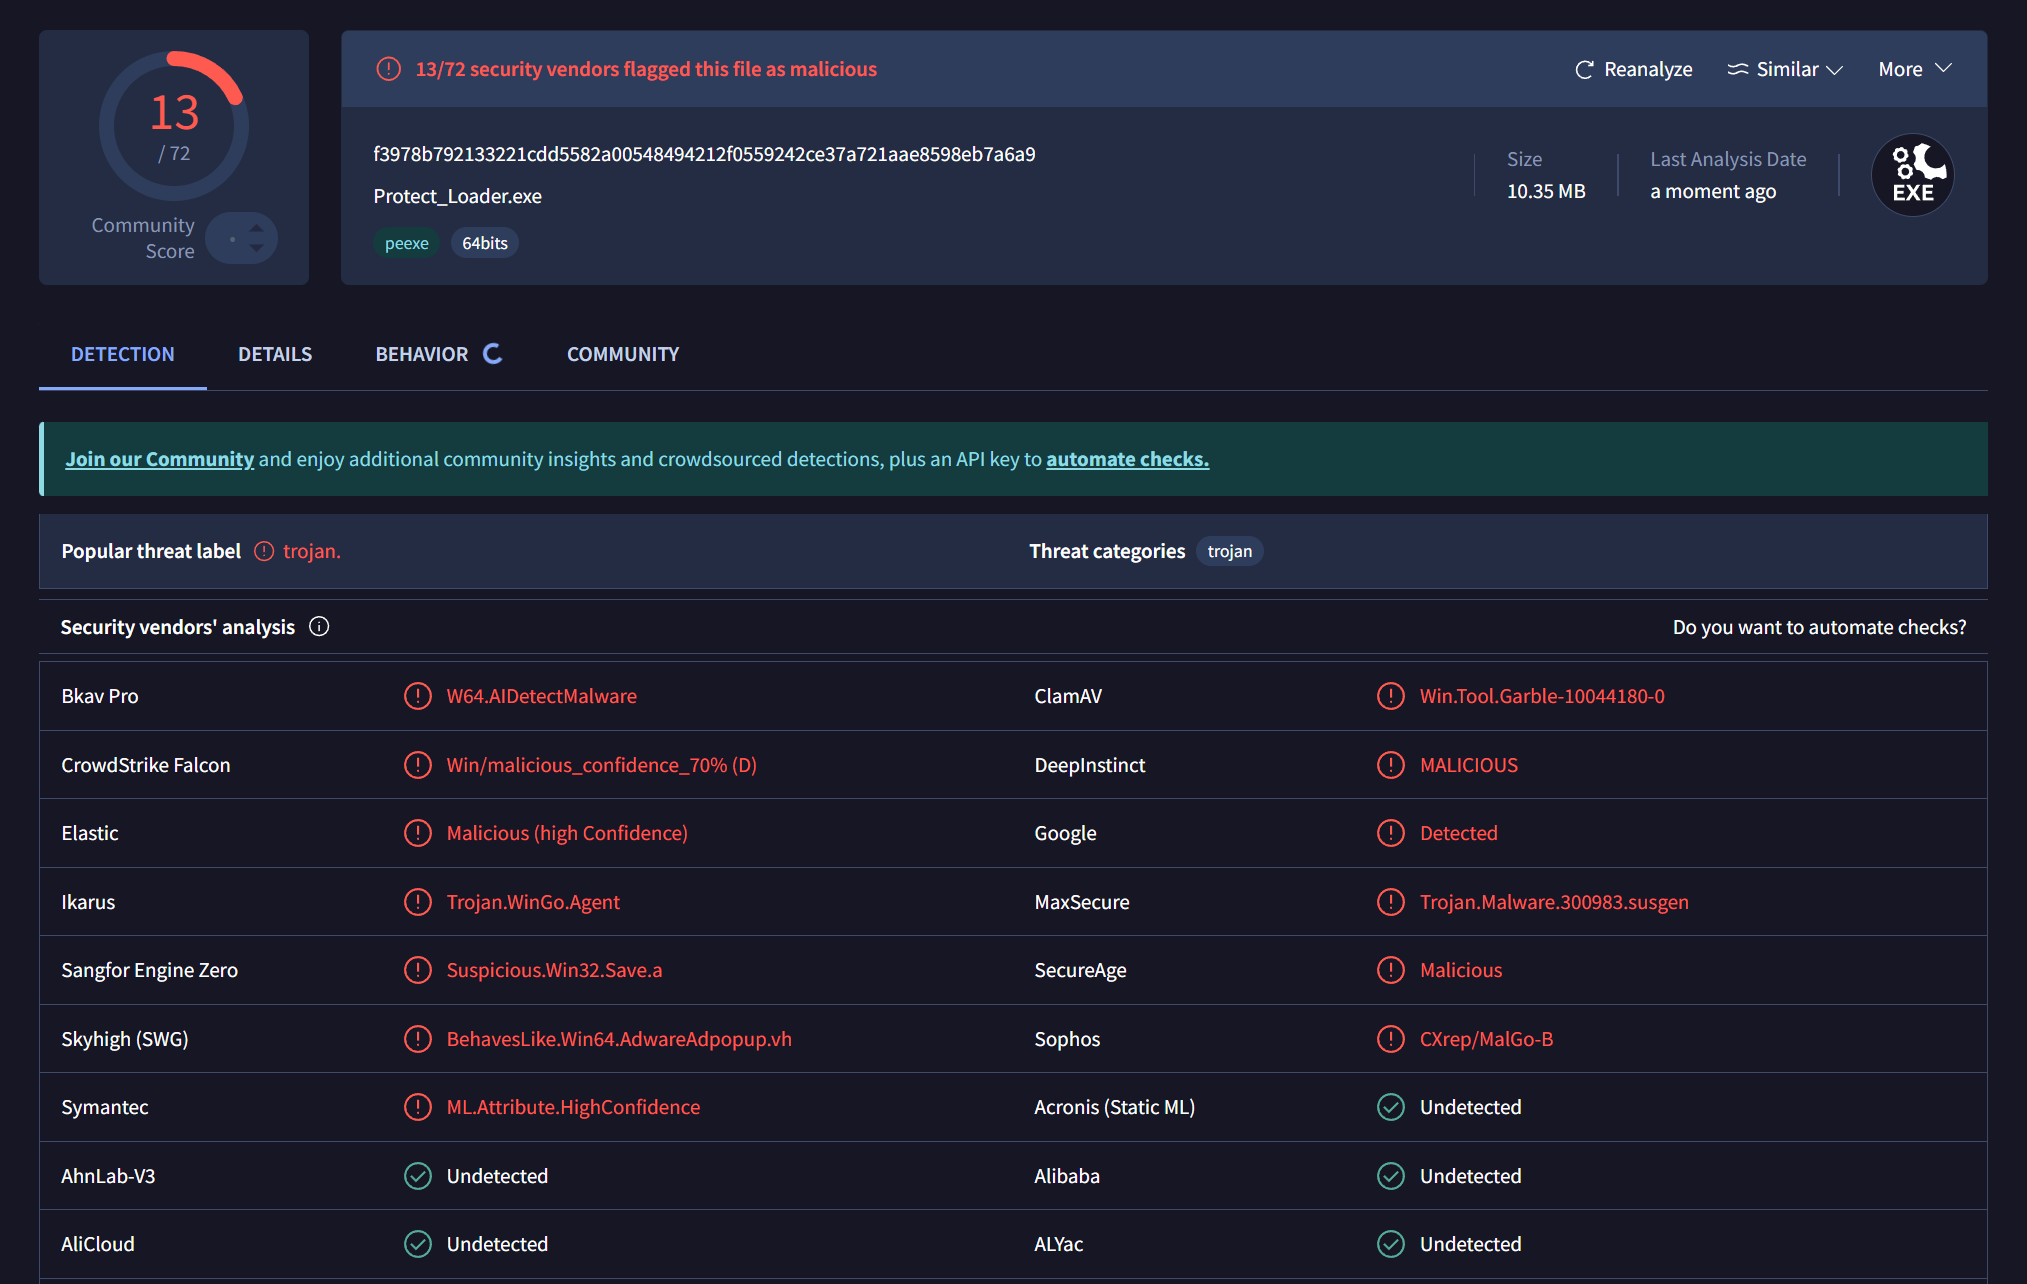
VirusTotal The detection is done without anti debug/vm there will be NO update against detection rate,this is done with a reverse shell.
-
Avast one Runtime:

- This tool is entended to be used for educational purpose,I don't take any responsability about what you do with this software (and should be not used since its unstable)
This Project is licensed under CC BY-NC 4.0